# Add authorization token creation endpoint to Lens Spaces API
**URL:** https://forums.k8slens.dev/t/add-authorization-token-creation-endpoint-to-lens-spaces-api/2846
**Category:** Feature Requests
**Created:** [February 14, 2024, 4:12pm UTC](https://forums.k8slens.dev/t/add-authorization-token-creation-endpoint-to-lens-spaces-api/2846 "2024-02-14T16:12:16Z")
**Posts on this page:** 6
**Page:** 1
### Author:  [@ccittadino](https://forums.k8slens.dev/u/ccittadino)
#### Post date: [February 14, 2024, 4:12pm UTC](https://forums.k8slens.dev/t/add-authorization-token-creation-endpoint-to-lens-spaces-api/2846/1 "2024-02-14T16:12:16Z")
We are using cluster connect (bored agent) to support a dynamic set of edge devices. This means we need to automate the creation of cluster connect tokens. The API supports this with a valid Authorization header, but the API has no way to generate the Authorization header.
Workaround is currently to log into Lens ID and pull the Authorization header out of the browser developer console. This token only lasts 8 hours though, so we’re working to programmatically log in via a mock browser of some kind. This is obviously not ideal, and a gaping hole in the API design.
---
### Author:  [@hchen](https://forums.k8slens.dev/u/hchen)
#### Post date: [February 21, 2024, 8:25am UTC](https://forums.k8slens.dev/t/add-authorization-token-creation-endpoint-to-lens-spaces-api/2846/2 "2024-02-21T08:25:21Z")
Ideally we should add support for api-key system, but in the meanwhile maybe you can try use the refresh token (not the access token you got from Authorization header)
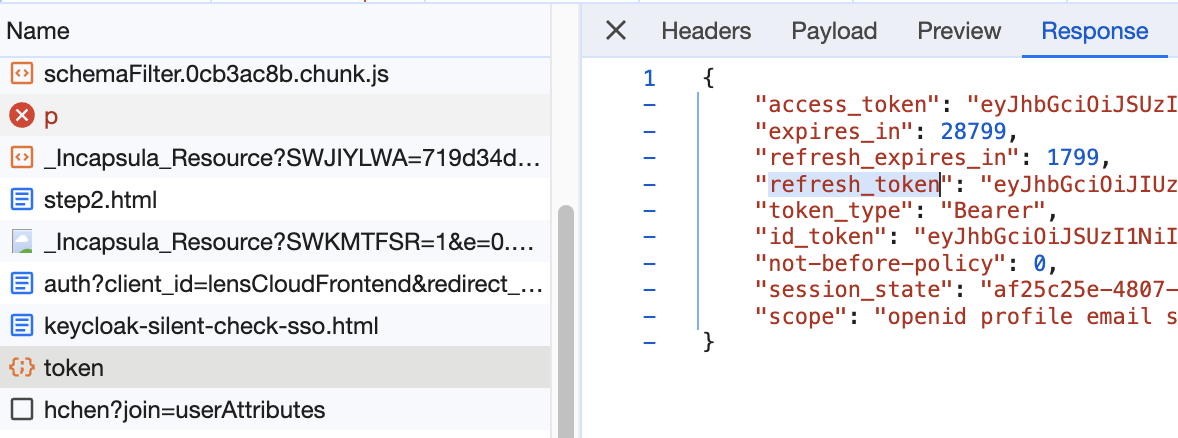
to get a new access token every 8 hours, the renew token endpoint is `https://app.k8slens.dev/auth/realms/lensCloud/protocol/openid-connect/token`
and use the access token in Authorization header to interact with our APIs.
Full openid-config [https://app.k8slens.dev/auth/realms/lensCloud/.well-known/openid-configuration](https://app.k8slens.dev/auth/realms/lensCloud/.well-known/openid-configuration)
---
### Author:  [@ccittadino](https://forums.k8slens.dev/u/ccittadino)
#### Post date: [February 21, 2024, 3:54pm UTC](https://forums.k8slens.dev/t/add-authorization-token-creation-endpoint-to-lens-spaces-api/2846/3 "2024-02-21T15:54:35Z")
> [@hchen](#):
>
> use the refresh token (not the access token you got from Authorization header)
Sorry I’m not following here, these statements seem at odds;
You said → “use the refresh token (not the access token you got from Authorization header)”
and then → “and use the access token in Authorization header to interact with our APIs.”
Also, if I have to programatically pull out the authorization token _in order to get_ the refresh token, what good is the refresh token helping me with exactly?
---
### Author:  [@hchen](https://forums.k8slens.dev/u/hchen)
#### Post date: [February 21, 2024, 4:26pm UTC](https://forums.k8slens.dev/t/add-authorization-token-creation-endpoint-to-lens-spaces-api/2846/4 "2024-02-21T16:26:21Z")
Hell, the refresh token is the token you use to renew an access token, the access token is the token you use to interact with our APIs, the one you pull from the Authorization header is the access token, which expired every 8 hr, but the refresh token does has a longer life span (don’t how long but you can decode the token and check the `.exp` value).
---
### Author:  [@ccittadino](https://forums.k8slens.dev/u/ccittadino)
#### Post date: [February 21, 2024, 4:40pm UTC](https://forums.k8slens.dev/t/add-authorization-token-creation-endpoint-to-lens-spaces-api/2846/5 "2024-02-21T16:40:38Z")
It says “expires\_in” is 8hours and “refresh\_expires\_in” 30min so… the refresh token expires quite a bit sooner? Odd.
In any case, can you send us an example of calling the token refresh API please?
---
### Author:  [@ccittadino](https://forums.k8slens.dev/u/ccittadino)
#### Post date: [February 21, 2024, 8:06pm UTC](https://forums.k8slens.dev/t/add-authorization-token-creation-endpoint-to-lens-spaces-api/2846/6 "2024-02-21T20:06:42Z")
Answered my own question by digging in with the dev console:
```plaintext
'https://keycloak.k8slens.dev/auth/realms/lensCloud/protocol/openid-connect/token' \
-H 'accept: */*' \
-H 'Content-Type: application/x-www-form-urlencoded' \
-d 'grant_type=refresh_token&refresh_token=REDACTED&client_id=lensCloudFrontend' | jq
```
The above call will return a new refresh-token and access-token.